Security Reviews
Security review is the practice of checking code, dependencies, secrets, and AI-generated changes before they reach important branches or releases.
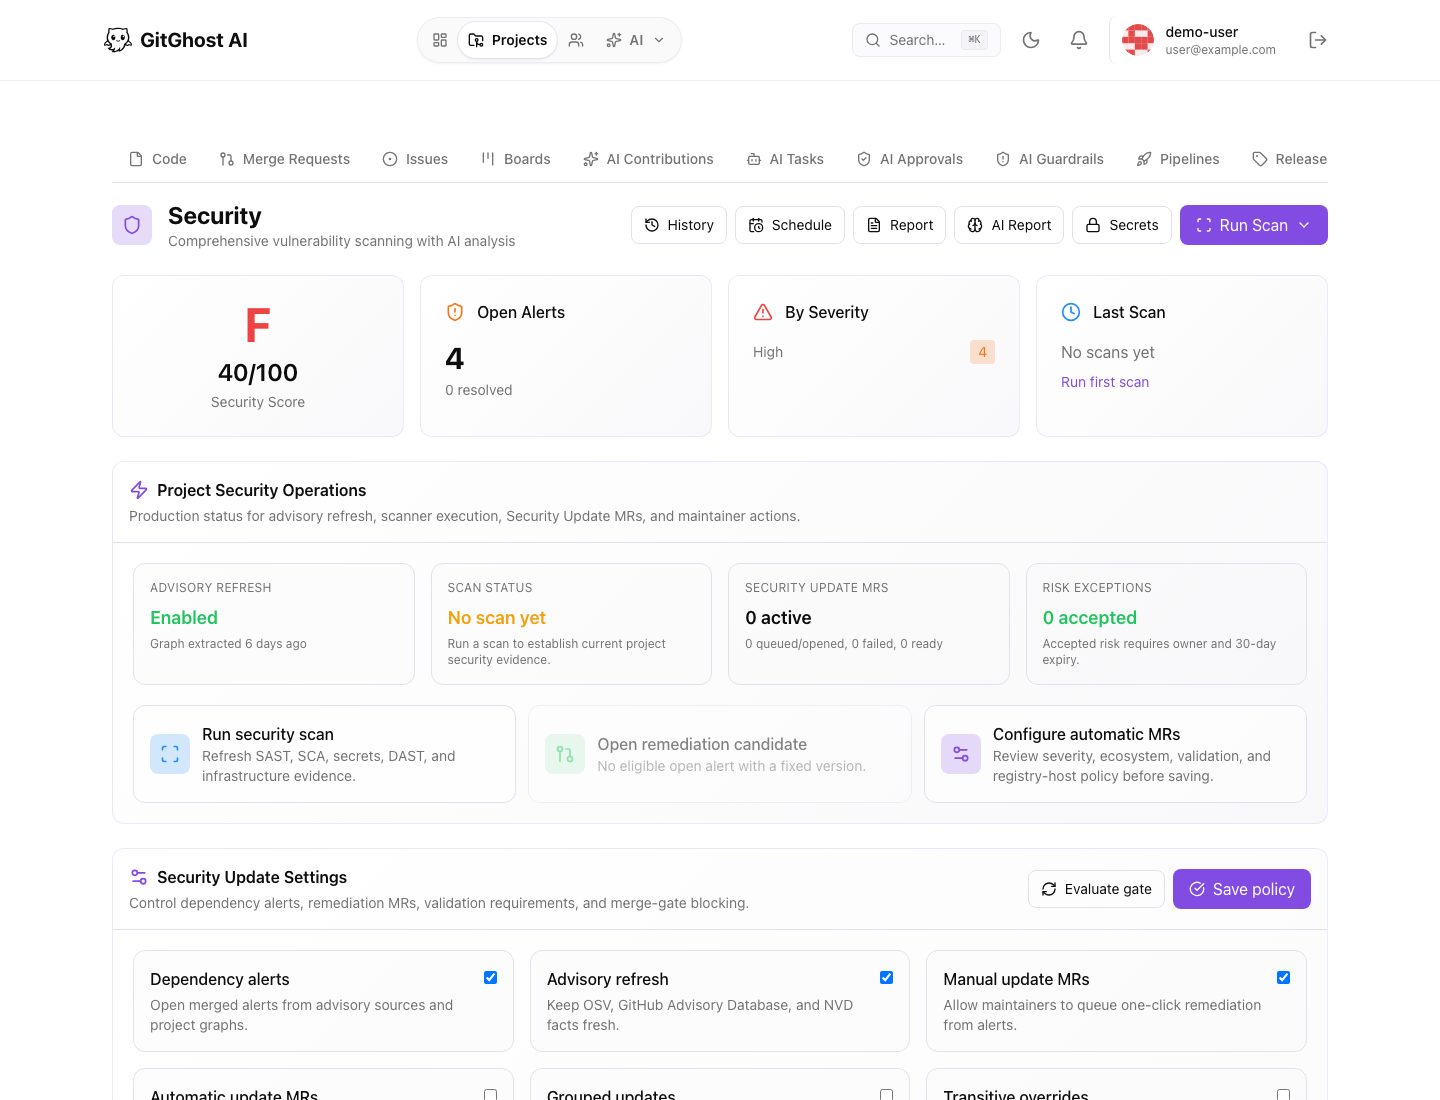
Start In The Security Center
Use Security Center for the complete project security workflow: score, scans, alerts, dependency intelligence, project secrets, and remediation work.
Review Checklist
For each proposed change, check:
- The issue or request that started the work.
- The file diff.
- Pipeline status.
- Security alerts.
- Dependency changes.
- Project secrets touched by the workflow.
- AI transcript, checkpoints, or action requests when AI helped.
- Approval requirements.
Security Findings
For each finding:
- Read the affected file, package, or component.
- Check whether the finding is real.
- Fix real issues before merging when possible.
- Use accepted risk only when the team understands and owns the risk.
- Record false positives clearly so they can be revisited.
AI-Generated Work
Before accepting AI-generated work:
- Confirm the prompt and task scope.
- Confirm the agent did not exceed policy.
- Review generated code manually.
- Confirm validation evidence exists.
- Confirm the merge request links to the right issue or session.
Sensitive Data
Do not paste secrets, private keys, customer data, private logs, or incident details into issues, prompts, merge requests, release notes, or public screenshots.